One-Click Auth
One Engine. Two Deployment Modes. Zero Custom SDKs.
Experience seamless One-Click Authentication-as-a-Service using a secure, one-time login link or OTP.
Engineered for rapid integration using standard OIDC and PKCE protocols.
Fast and lightweight. Try Me to quickly see how smooth the flow is !
#One-Click-Auth is our flagship product to achieve a more secure and seamless login without the hassle of remembering passwords or being exposed to hacking attempts.
The login is as simple as entering an email address and clicking the link received in their inbox.
Alternatively, we also support OTP based authentication, as part of the same process, to help ease the login process further for our Customers.
One-Click Authentication is completely secure even for client-side-only apps like Single Page Applications.
Being an OpenID compliant Identity Provider using PKCE means Integration is Plug-and-Play by pointing your existing code easily to Éclat Blue.
Best of all, One-Click Authentication is free for hobby projects or projects with limited users/login requirements.
▶ Deployment Modes
Server-less
The entire authentication lifecycle is handled directly within the browser runtime environments using the standard OIDC/PKCE protocol.
How it operates: The single-use authorization code is requested and exchanged client-side using a locally generated verifier challenge.
Best For: SPA and early prototypes
The Advantage: Completely safe for SPA and allows authentication with zero server instances to configure, maintain, or manage.
Server-based
Retain the ultra-smooth routing flows and instant UI state transitions of your SPA callback layer, but execute the critical token request behind a secure proxy.
How it operates: The client-side initiates the login and your backend exchanges the code for a token to securely and seamlessly transition to a cookie-based auth for ease and added security.
Best For: For systems with backends that require added security and ease.
The Advantage: Tokens never touch browser local storage thus eliminating client-side XSS injection hazards entirely.
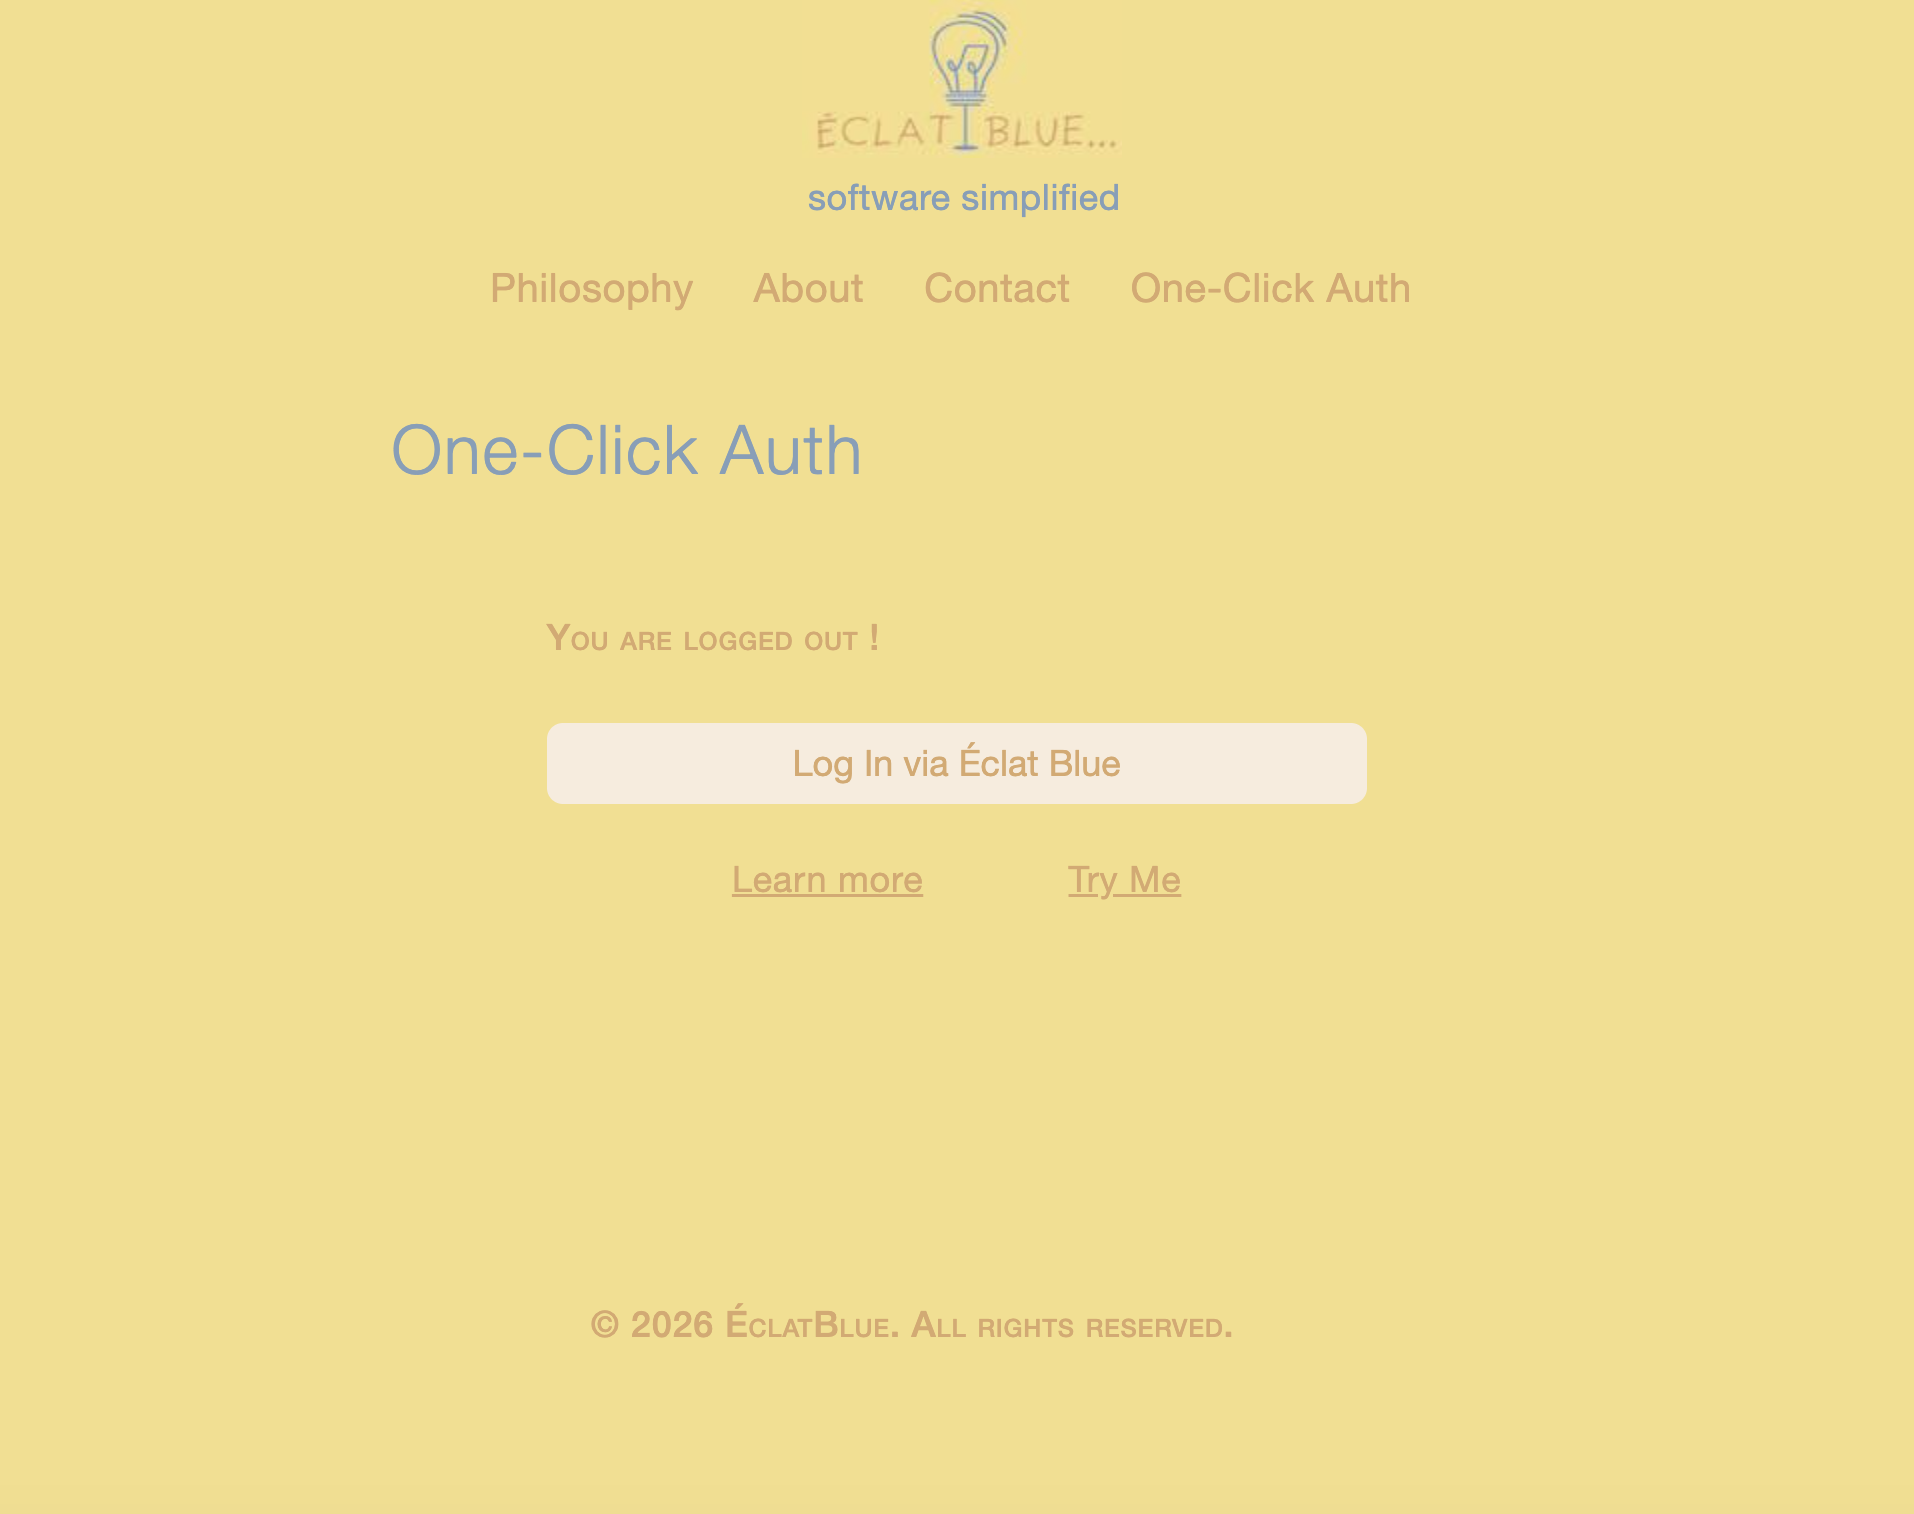
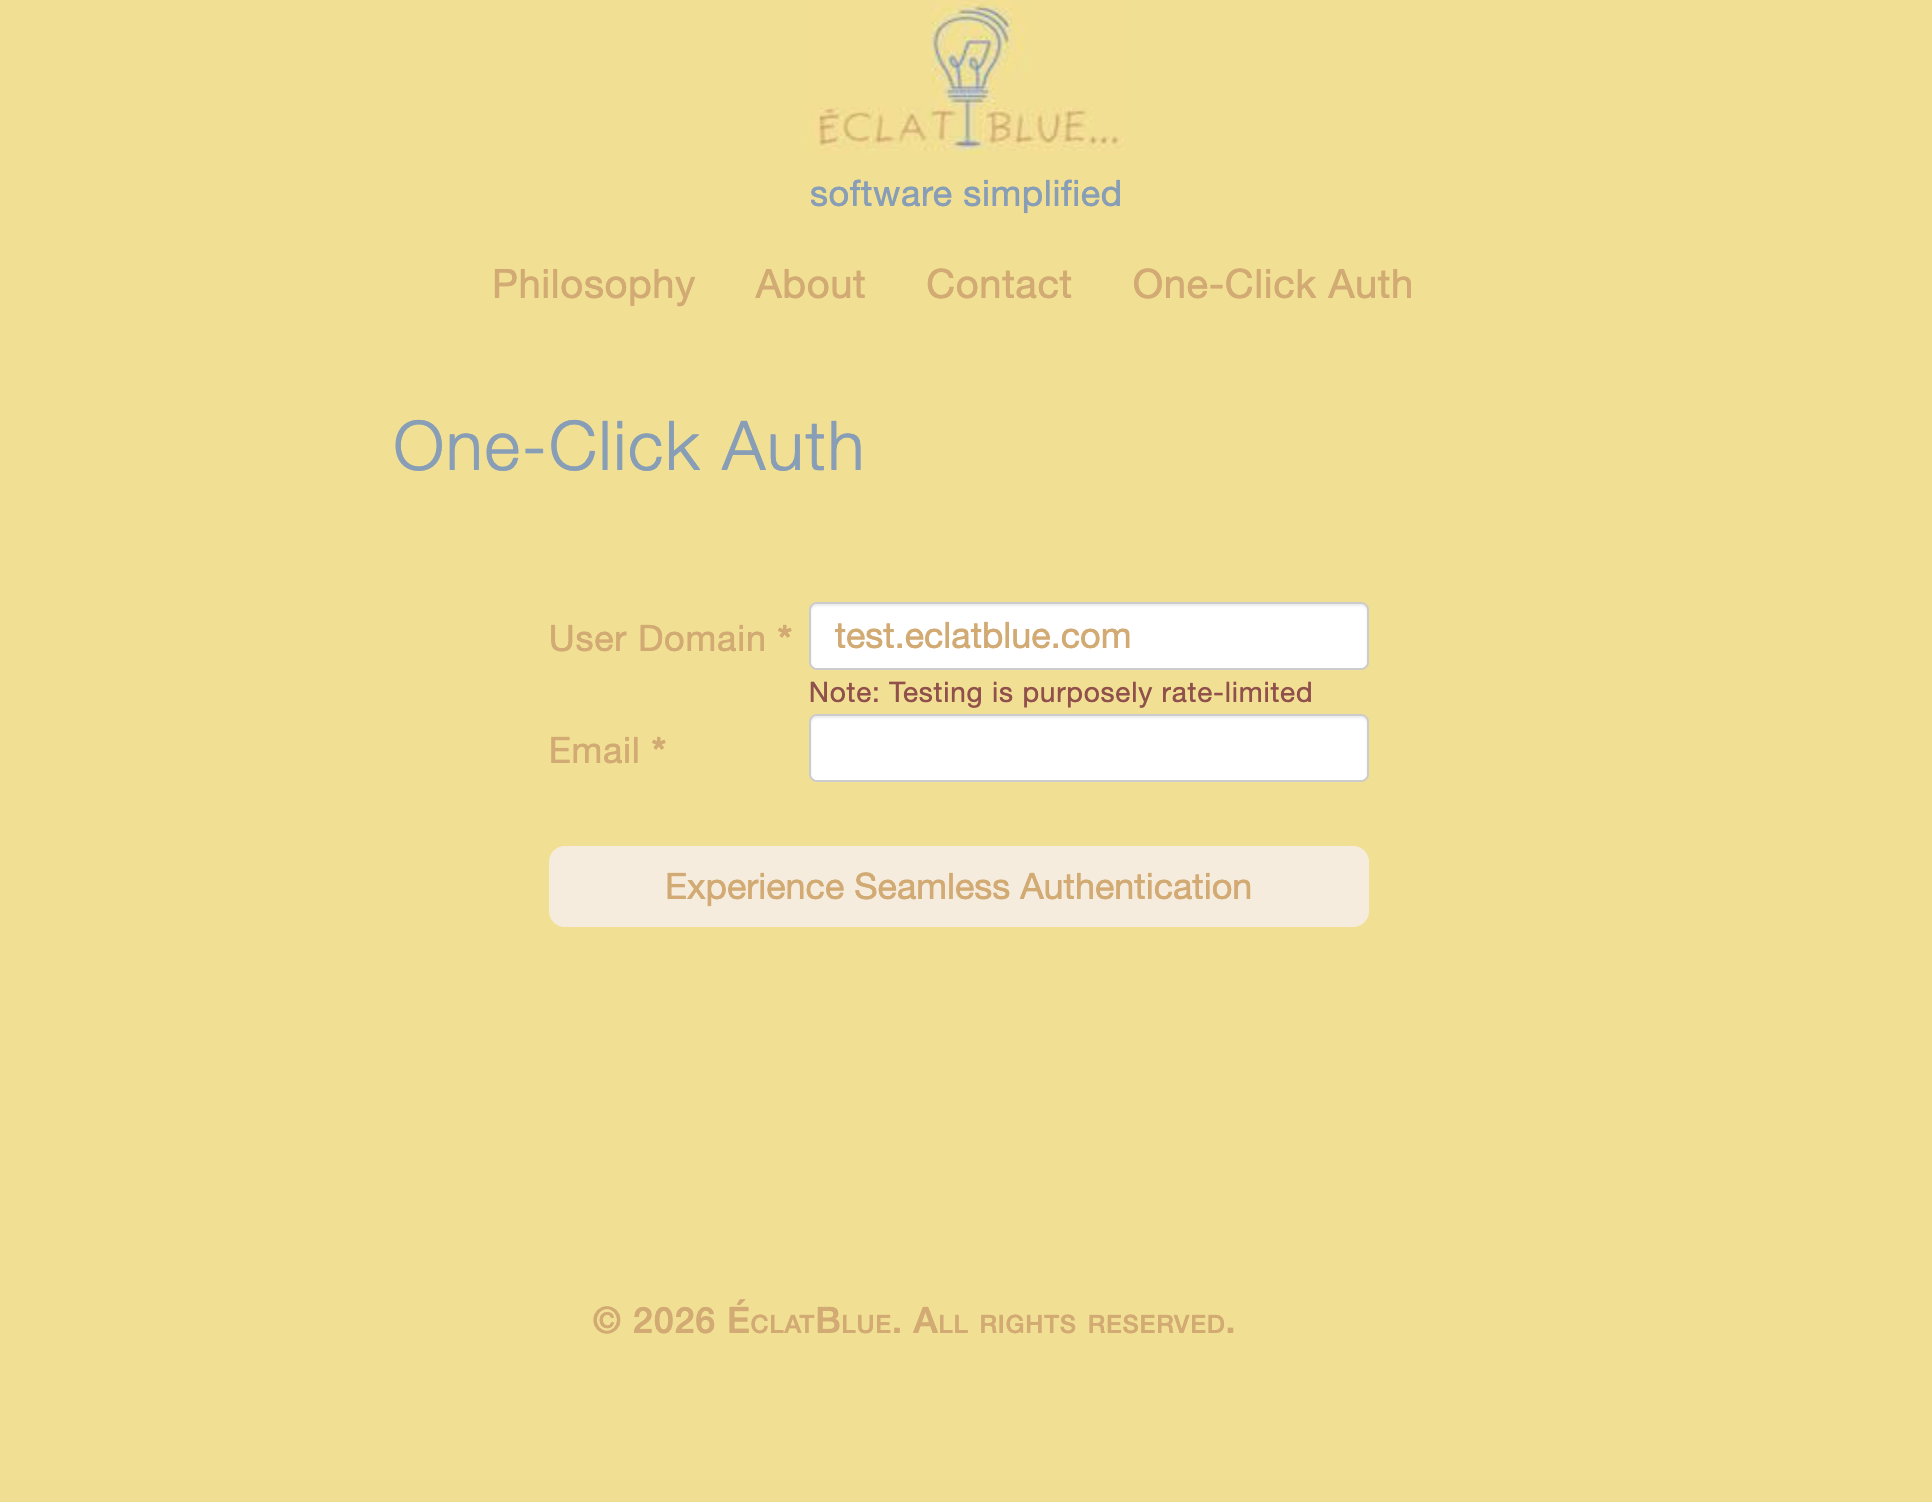
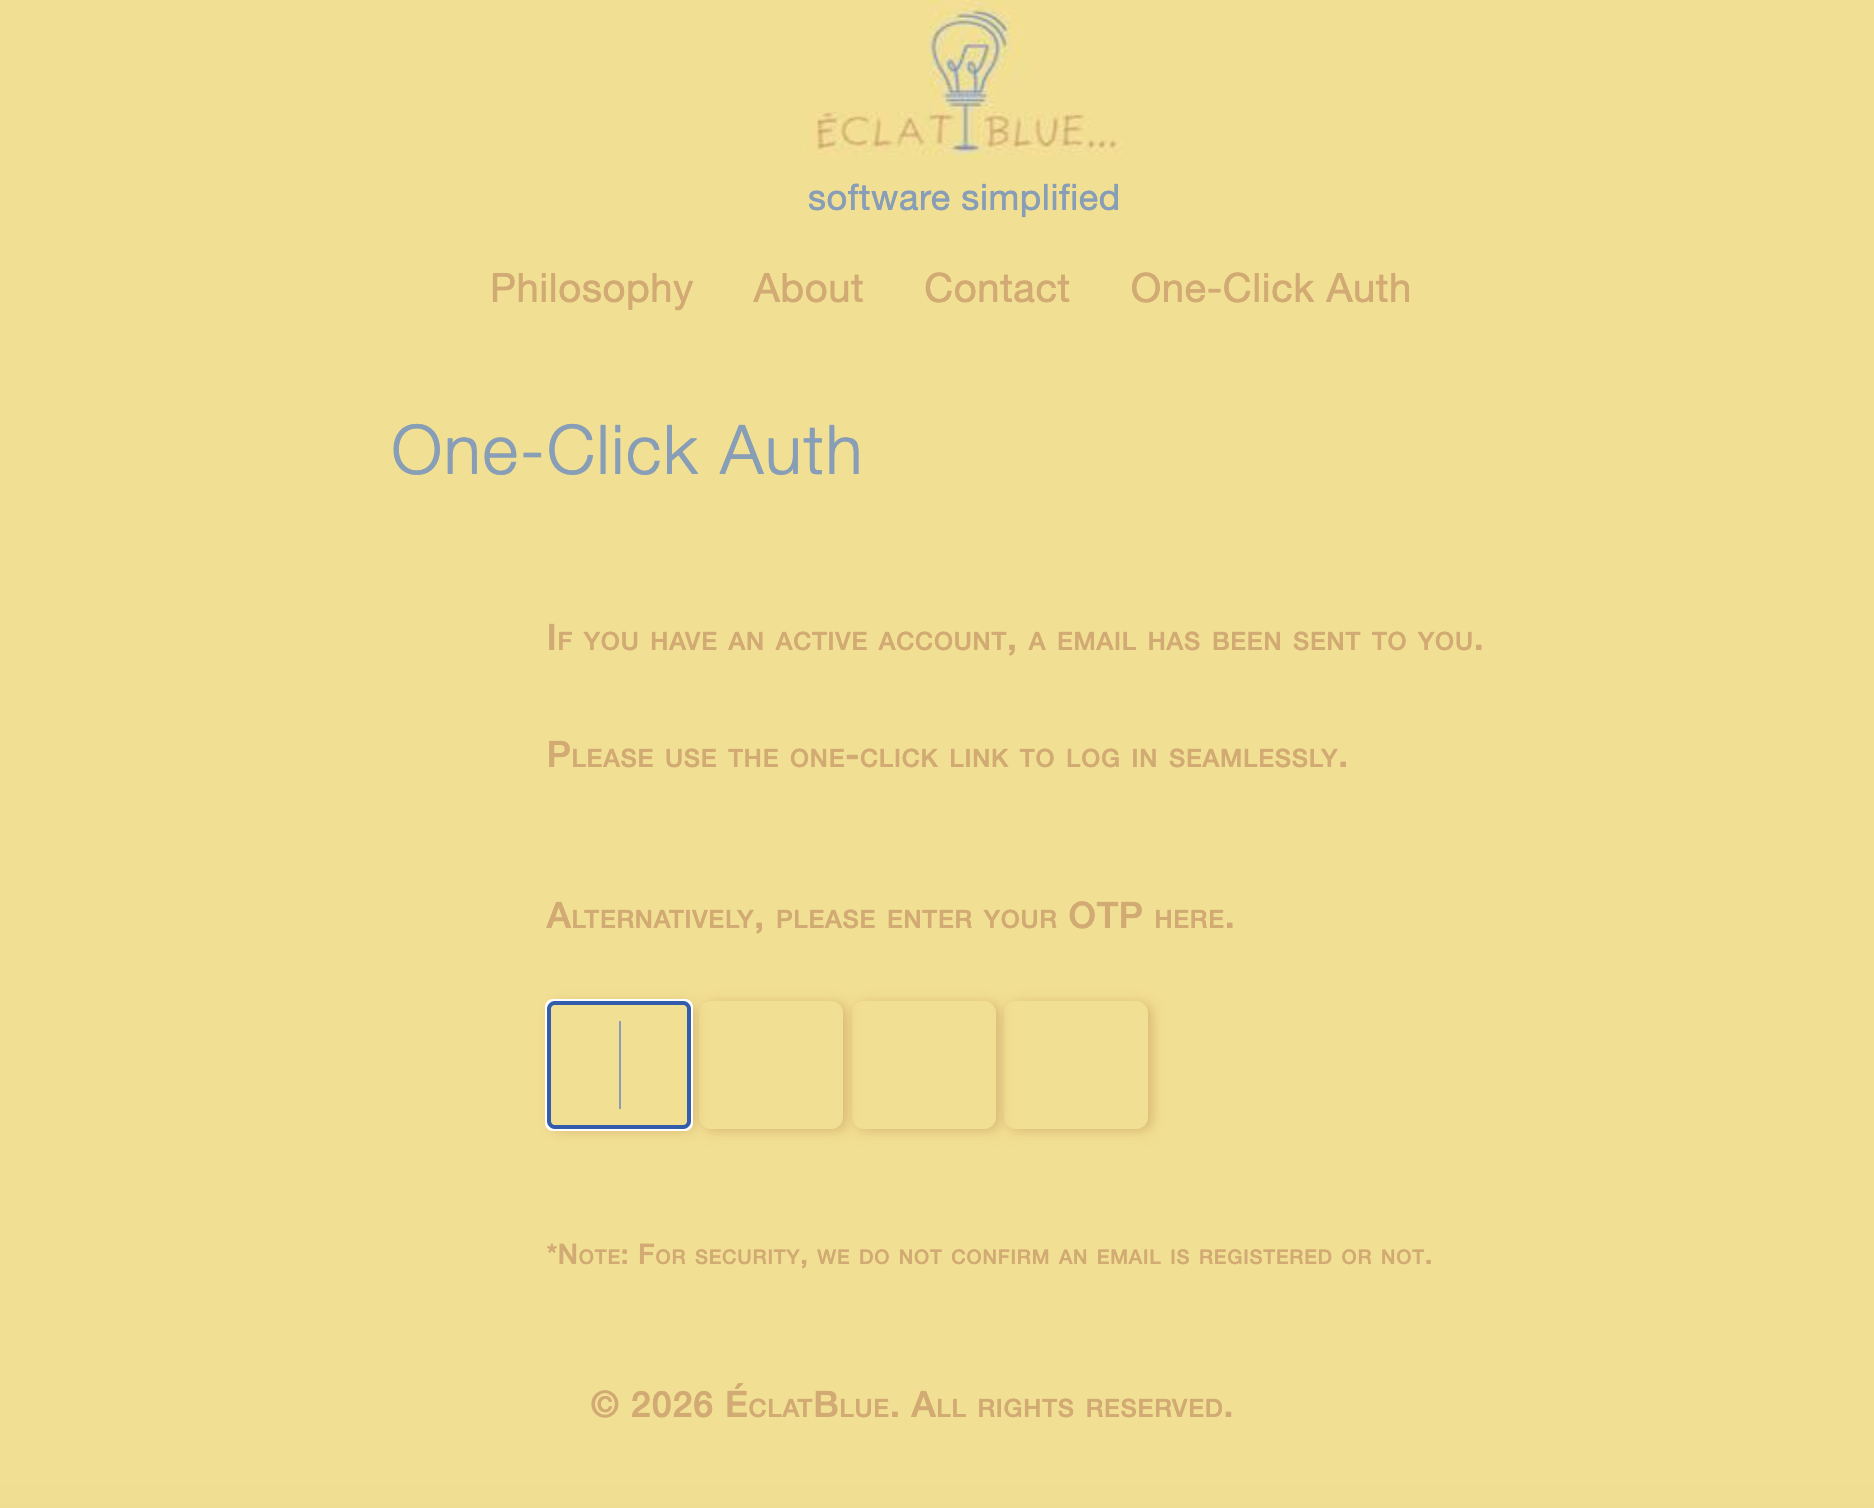
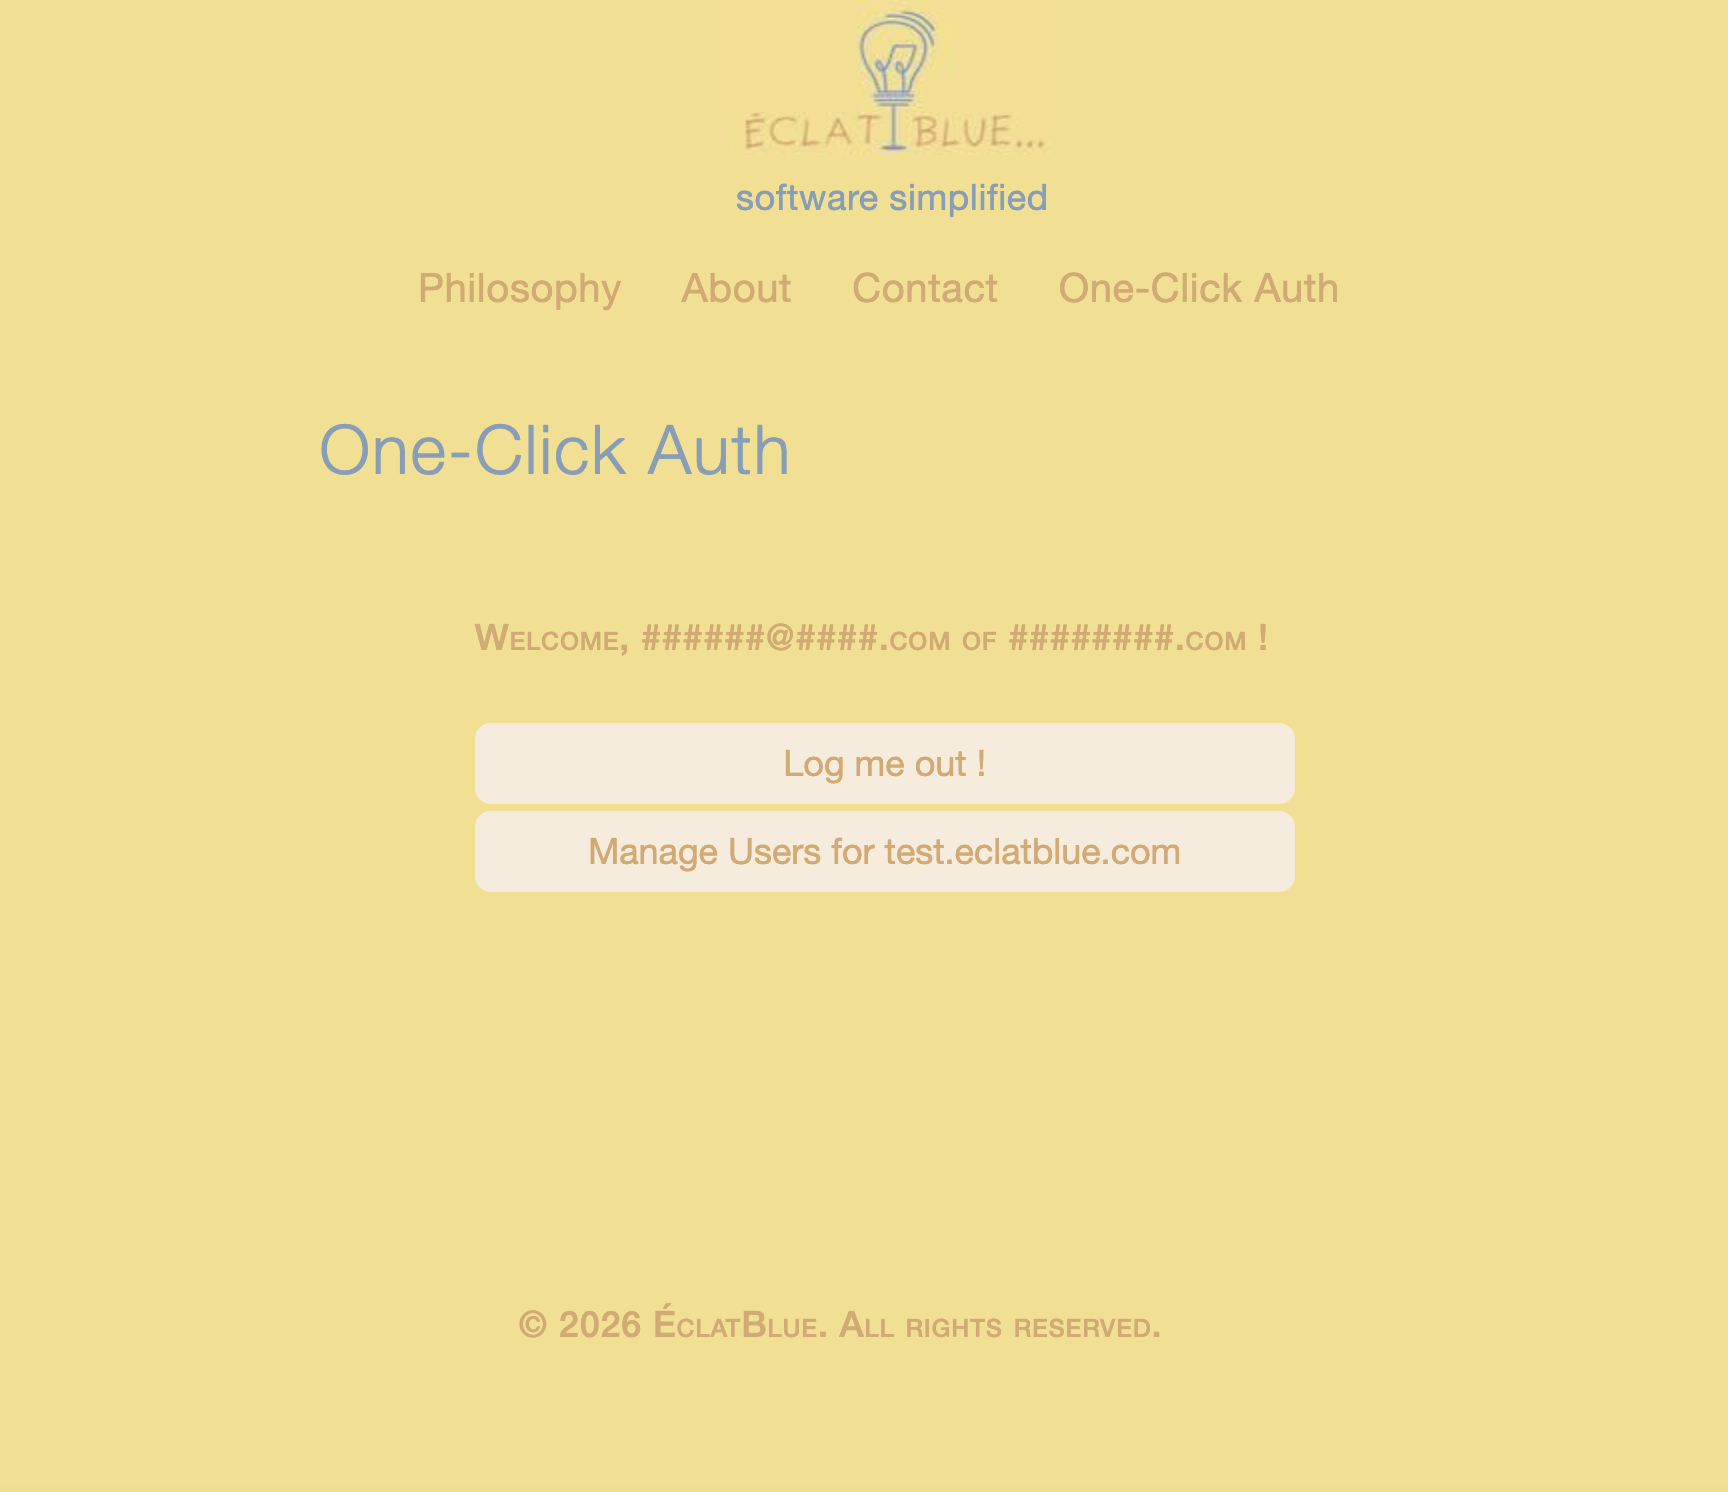
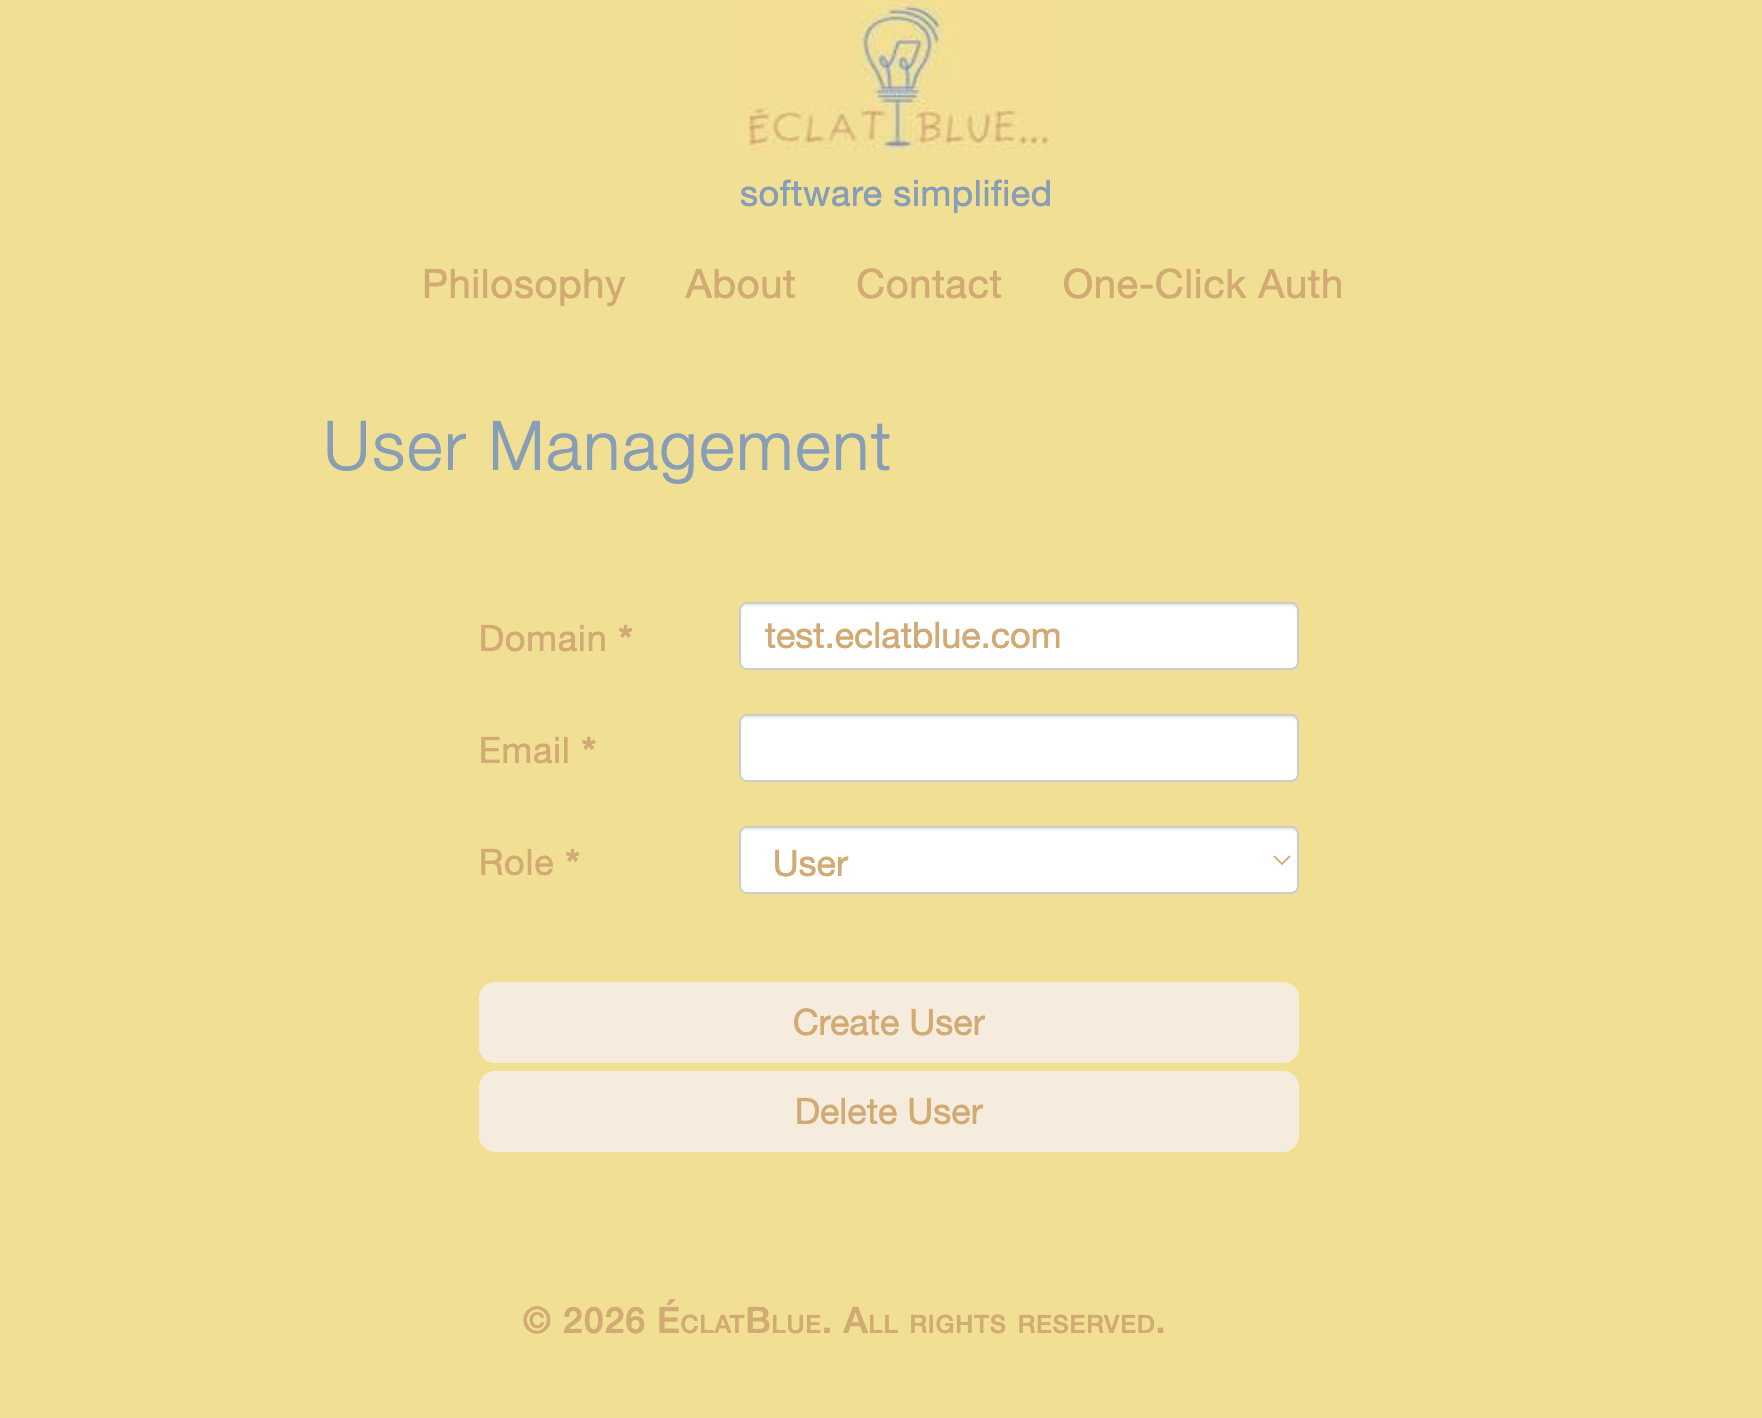
▶ View the Authentication Flow in Screenshots
▶ Security & Architecture FAQ
How is Authentication done?
We authenticate a user/email by sending a One-Click link and OTP to your email address. The idea is that only you will have access to your email address to prove these details back to us.
How secure are the magic links and OTP delivery paths?
Every magic link payload is fully tokenized and protected using strong cryptographic encryption. Furthermore, if a user opts for the OTP flow, the temporary session state tracking is also encrypted directly within the URL parameter. This approach ensures the entire lifecycle remains completely stateless and tamper-proof.
Is client-side authentication truly secure for Single Page Applications (SPAs)?
Yes. By strictly enforcing the OpenID Connect (OIDC) protocol paired with Proof Key for Code Exchange (PKCE), Éclat Blue eliminates the need for exposing static client secrets in frontend applications.
How is user management handled?
By default, any user can authenticate as a standard user, which you can decide how to manage within your code. However, if you choose to manually add users via our user management portal (for admins), your domain switches to a restricted list. Only explicitly managed users will be allowed to log in; anyone not on the list will be blocked. So, both modes are available and you can choose which one suits your purposes.
How are user sessions renewed?
User sessions are silently and securely renewed in the background so as to minimize interruptions to your users using Refresh Token Rotation (RTR) The values of how short or long sessions should be and their renewals can be configured as per your request.
Do you have user session revoke facility?
Yes, we automatically revoke access on suspicious login/refresh-token activity (eg stolen session / replay attacks), on user logouts and on demand using our self-serve users portal for administrators.
Do you work with us to help us implement best practices?
Yes, we will help support you to ensure you are fully ready to go.
Do you handle Autorization also?
No, we only ensure validation of user emails ie the user authenticity (using JWT tokens) only. Authorization, you are free to implement based on our secure tokens or by using our Bridge to your token system.
Do you save my user's data?
We save user email address to maintain active sessions for their security and to cover security usecases like revoking access on replay attacks. Apart from this, we also save user email addresses if you opt in to the user white list mode of authentication through the user management portal.
Do you share my user's data with anyone?
No, we do not share data with others, except while sending emails - which requires us to share the email with our service provider.
What are the usage limitations on the free hobby tier?
Our philosophy is centered around simplifying software deployment for independent developers. The free tier is designed to support early-stage and hobby applications with a practical limit on active users and monthly login transactions, giving you full access to standard protocol features without any initial financial overhead.
How do I register a domain wih you?
At the moment, it is manual request through the contact form so that we can fully understand your requirements, support you to integrate and create your administrator account. However, for the free tier we are also working hard to automate domain registrations soon based on validation of domain ownership. We will keep you informed!
Any option to present the login screen using my branding?
This is a nice feature that we are exploring, let us know if you are interested.
Are there any Security Validations done?
Last Security Validation was done in September 2026 using Automated (ZAP) Web Application Security Scan (DAST Framework).
Since the callback URL hits the SPA client browser space first, is the system exposed to XSS?
No. The authorization code delivered to the URL parameters bar is an ephemeral, single-use token valid for minutes. Because Éclat Blue mandates strict PKCE challenge protocols, an attacker cannot intercept or use the code without knowing the underlying raw cryptographical key value. The moment your backend claims the code, it is instantly revoked globally.
I have suggestions or feedback?
We will be happy to hear from you. Please use the Contact form to reach out.